
Identity Provider (IdP)
Serves as the trusted source for access across all user types and target resources. Junto empowers authentication and authorization to be as powerful, granular, and flexible as your unique needs demand. Junto supports all popular methods including passwords, biometrics, and multi-factor authentication (MFA).
Granular Access Control
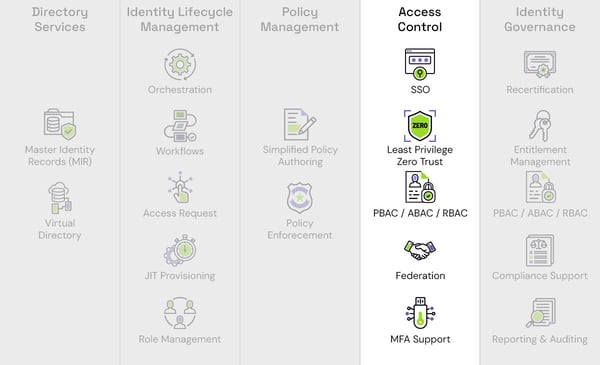
Enhance security and data protection with flexible, context-aware access control based on policies that can adapt to varying conditions, any type of user/identity, and all target systems (for example critical infrastructure and agentic technologies). With Junto access or denial happens in real-time without the need to log off and back on for enforcement. Junto delivers extremely flexible and granular control of access permissions utilizing policies (PBAC), attributes (ABAC), or roles (RBAC) associated with users, systems, and the environment to make access decisions and enforce controls.
Access Policy Enforcement
Ensure that only authorized individuals or identities gain access to systems. Junto enables dynamic and zero trust access control decisions that allow authorized entities precisely the correct access to resources at any time and from anywhere. Includes support of authentication and authorization assertions including:
• Conditional access
• Step-up authentication
• Time-bound access
• Just-in-time access
• Least privilege access
• Dynamic access
Single Sign-on (SSO)
Remove access barriers without sacrificing control or security. Junto empowers users to securely and appropriately access multiple applications or systems with a single set of login credentials. Its full SSO functionality includes support for:
• Federation
• Kerberos
• SAML
• OIDC
• OAUTH2
• Reverse proxy for legacy systems
Persistent Authentication
Raise the security bar without disrupting operations or obstructing user productivity. Junto verifies authenticators each time the authentication token is used to ensure the right access for the right identities to the right resources every time – no compromises.
Multi-factor Authentication Support
Junto’s “bring your own MFA” approach enhances security by adding an extra layer of protection against unauthorized access, ensuring SSO does not become a single point of vulnerability. Whatever MFA option you need to use is supported without difficult integrations of technological compromises. Junto supports all of the most popular MFA standards:
• CAC/PIV
• FIDO2 tokens
• Certificate-based authentication